Zero-Knowledge Security by Default
Every SimpleViewer session is protected by end-to-end AES-256-GCM authenticated encryption, salted SHA-256 challenge-response handshakes, and granular host-side permission gates.
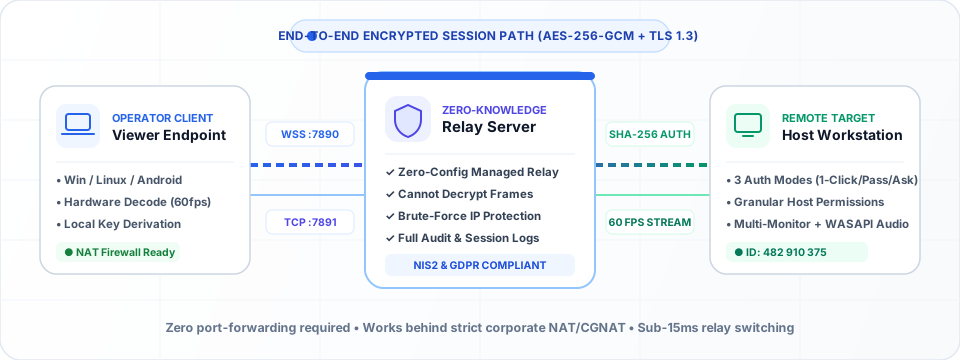
AES-256-GCM Payload Encryption
Screen frames, audio streams, file transfer chunks, clipboard sync, and remote terminal I/O are encrypted on the endpoint before transmission. The relay server routes opaque binary frames and cannot decrypt session content.
Salted SHA-256 Challenge-Response
Neither temporary 6-character passwords nor permanent unattended passwords are ever transmitted over the network. Endpoints exchange cryptographic proofs over TLS 1.3 with per-session salts and nonces.
Automated Brute-Force Quarantine
Both host clients and the signaling server enforce strict IP rate limiting: 5 failed password attempts trigger an immediate 15-minute IP block (429 Too Many Requests).
Managed Security & Optional Business Self-Hosting
By default, all SimpleViewer sessions connect seamlessly through our managed relay infrastructure with end-to-end encryption. For Business and Enterprise subscribers with strict internal compliance requirements, an optional dedicated self-hosted relay setup is available—contact us for more information.
- SHA-256 binary integrity verification on all client downloads (
/api/health) - Granular interactive host consent (Mouse/Keyboard, File Transfer, Clipboard, Audio)
- Instant session termination via host popup or Central Web Admin Console